
← All posts
Engineering
Fundamentals of a secure IoT solution
Security is the single most underestimated area in IoT services, and far too often treated as an afterthought.
3 min read

We consider security to be the single most underestimated area within IoT based services, and it is far too often treated as an afterthought. This could prove to be a risky approach, and is an opportunity for people with cruel intentions. Cobira strongly recommends a thorough assessment of your IoT solution security design. Security aspects shall preferably be considered and designed from the very beginning of the process, along with all other aspects such as device, firmware configurations, connectivity, and cloud. But it is never too late to consider security improvements in your deployed installations.
But my service does not contain critical infrastructure
It is tempting to dismiss the risk of being attacked because you think your service is uninteresting for hackers. It does not contain sensitive information and does not give access to critical infrastructure. This is obviously to some extent also valid, but it is more important to consider every service to be the potential target of an attack.
But my IoT device does not use a mainstream operating system
While it is true that mainstream operating systems like Windows, and to some extent BSD and Linux based distributions, are a prime target for many viral and cybercriminal attacks, it does not mean that not using one of the above would exclude you from being subject to attacks.
Then what?
In many aspects the perfect secure IoT solution can be thought of as nirvana. And this is true in the sense that it is a continuous strive towards the best possible security level. On the other hand, the saying “the enemy of good is better” is also true. So the best possible advice is to take a balanced and proportionate approach, and a good solution is by far better than no solution.
Standard is the way to go
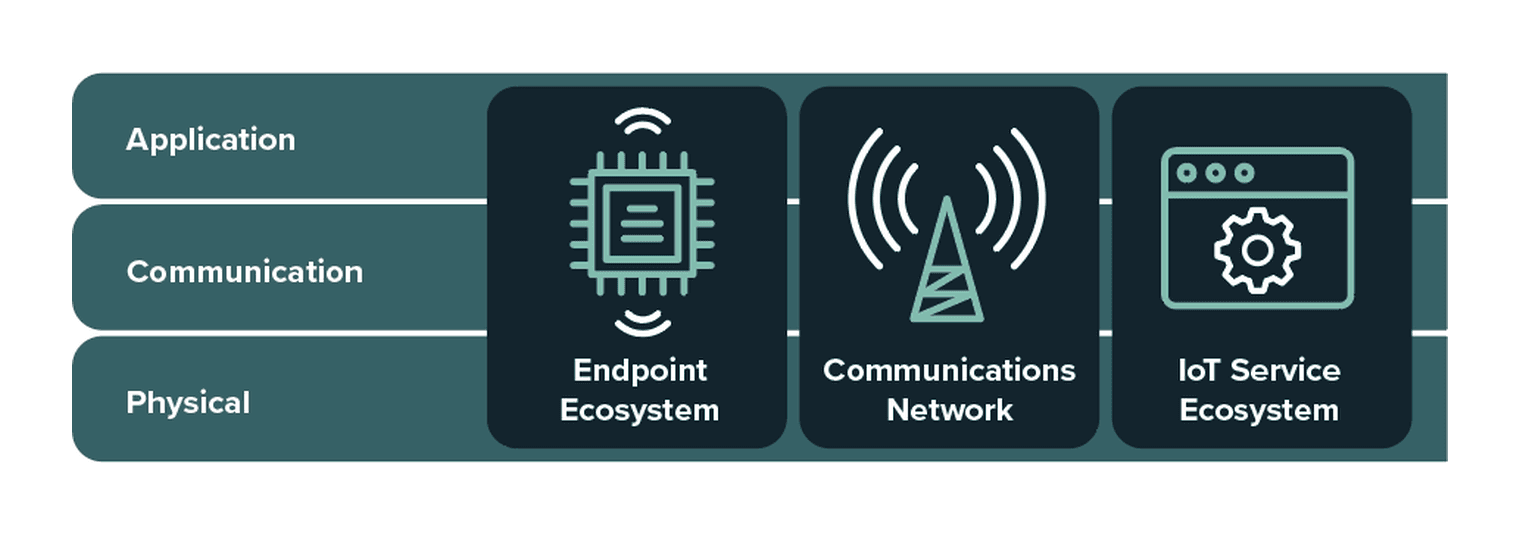
In recent years there has been increased work with standards in security for IoT solutions. Bodies such as OWASP, GSMA, IEEE, NIS and CSA have driven and published a lot of material on this subject. If we take GSMA as an example, they have a break-down of the security model of an IoT solution vertical in three main areas: endpoint, networks and platform. For these three main areas, there are three layers: physical, communication and application.
The key to all good security designs is a structured approach, and it is important to lean on a model that helps drive the right security architecture based on continuous threat analysis. This approach will assess the full lifecycle of any IoT solution, all the way from manufacturing through deployment to its operating phase.
Leap forward by using cellular connectivity
One easy step forward is using cellular connectivity, where you benefit from many years of standards maturing. GSMA and 3GPP have been putting a huge effort into ensuring safety and security in both traditional personal use and communication in IoT solutions.
This covers all elements, from the manufacturing of SIMs and the standards for the chips and secure elements used, to the security level in the interconnection between operators in roaming scenarios (IPX and GRX).
On top of this we offer value-added services like private and secure APNs, which are dedicated packet data networks where all cellular traffic terminates. Further routing of the traffic can be shielded and segregated from all other devices on the internet, to ensure device and cloud communication in your IoT solution stays within your security domain.
If you want to hear more about our view on IoT security, in this subject and others, we would be happy to set up a call.